Governance · Risk · Assurance
Governance, risk and assurance that works in practice.
We review what is actually working, design what should be, and build the risk, compliance and internal audit functions that make it real. Senior practitioners for boards, audit and risk committees, executive teams and the organisations they lead.
Evidence, not opinion.
What we do
Three questions we help answer
Most organisations come to us with one of three questions. Each engagement starts from that question, has a clear scope and an agreed fee, and ends when the answer is in your hands, not in a report on a shelf.
01 · Assess
Board and regulatory evidence review
“We believe we are compliant and well governed. What evidence would we produce if someone asked us to prove it?”
We test what is actually held rather than what is asserted: papers, decisions, controls and the assurance behind them. We map it against what you are accountable for, and show what is there, what is claimed but unsupported, and what is missing. You get findings written for directors, not specialists, and a practical 90-day plan.
What changes. Evidence you can put in front of a regulator, owner, funder or minister, and a clear view of where assurance is duplicated and where it is thin.
Who it's for. Boards and audit and risk committees, new chairs and chief executives asking what they have inherited, and organisations facing regulatory scrutiny or an adverse finding.
02 · Design
Transition, governance and risk roadmap
“We are becoming a different organisation. What has to be in place, who decides what, and in what order?”
For organisations being created, separated, merged or rebuilt. We design decision rights, committee structures, the risk framework and appetite, and an assurance model sized to what you can afford, then sequence it into a 6 to 12 month roadmap tested against the capacity you actually have.
What changes. Nothing falls between the old organisation and the new one. We know where obligations go missing in a transition, because we have found them afterwards.
Who it's for. Tertiary providers in transition, councils, council organisations and new water services entities, and Crown entities and newly established bodies.
03 · Implement
Implementation and assurance support
“We know what needs to change. We don't have the capacity or the independence to do it ourselves.”
We build risk, compliance and internal audit functions: policy, registers, risk appetite, charter, methodology, a risk-based plan and reporting the board can use. We run board and committee induction and workshops, design and test controls, and check that recommendations were actually closed. We also deliver individual internal audit reviews from your audit plan or ad-hoc, outsourced or co-sourced, including technology and programme assurance.
What changes. Recommendations become changes, not another report. When we build a function, we work alongside your people, hand it over, and plan our exit from the start.
Who it's for. New or restructured organisations standing up a function for the first time, and organisations with accepted recommendations and no one to deliver them.
Not sure which applies? Most conversations start with what is prompting the question. If a short, bounded review is the right answer we will say so; if it is not, we will tell you that too.
Changes we're helping with now
Where we're seeing demand now
Each of these changes raises one of the three questions above. Each item shows which offering it falls under.
FEATUREDPart of 03 Implement: board and committee development
Audit and risk committees in local government
Why now. Under the Local Government (System Improvements) Amendment Act 2026, from about 19 March 2027 non-elected members of council committees, including audit and risk committees and their independent chairs, no longer vote or count towards a quorum, with some exceptions (for example, members appointed under a Treaty settlement). They can still contribute their expertise, but the votes rest with elected members. In 2020, more than half of councils (54%) had an independent chair on their audit and risk committee. Before March, councils are reviewing terms of reference, membership, quorum and chairing; after it, elected members carry the committee's decisions. That is a change in capability as much as in rules.
Practical support to build confidence and capability for audit and risk committees and their members, using their council's own public papers, alongside LGNZ's training and the council's governance team. It is support for the committee, not an assessment of anyone on it.
The options can be combined, for example Chair-ready for the chair with Foundations for the deputy or other members.
Chair-ready
The usual place to start before March 2027. For whoever chairs, and the elected members who carry the votes: discussion of terms of reference, options for independent membership and chairing, quorum, a capability matrix for the chair and deputy, a practical work programme, running the meeting, and preparing questions for time with the auditors. A one-off package of two sessions of about 90 minutes, including preparation for the March 2027 changes. Follow-up meetings are separate, at additional cost.
Foundations
One-to-one sessions on risk, assurance and governance, each using your council's recent public papers as the worked example.
Meeting-ready
Before: we read the published agenda and send three to five questions tied to page numbers, then talk them through. After: we review later public papers for reported progress and, where the papers allow, identify further questions.
Committee workshop
2 to 3 hours for elected and independent members and governance staff, on the committee's own recent public papers. It ends with questions members may want to raise later.
What's different: built for councils · governance, risk and assurance together · every meeting, not just training · independent of the room: an external perspective without sitting on the committee, with conflicts assessed before and throughout each engagement.
Download the one-page overview (PDF)02 Design · 03 Implement
Water services reform
Councils are setting up new water services organisations. We help design their governance, decision rights, risk framework and assurance model, and set up risk and internal audit so they work from day one.
01 Assess · 02 Design
Tertiary and vocational change
Polytechnics are becoming standalone again and providers face new quality assurance expectations. We help map obligations through the separation, and give governing councils evidence that quality and risk systems are working.
About us
Three senior practitioners
Between us: board governance, regulated financial services and insurance, legal and regulatory review, internal audit and its quality assurance, and technology assurance. The people you meet do the work.
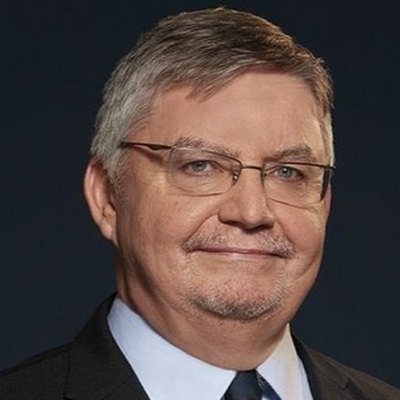
John Stewart
Internal audit, risk, compliance and governance
30+ years across regulated financial services, corporate and public-sector organisations. John delivers internal audit and assurance reviews, assesses governance and control frameworks, and reports to boards and senior leaders.
Approved external QA examiner · IIA facilitator
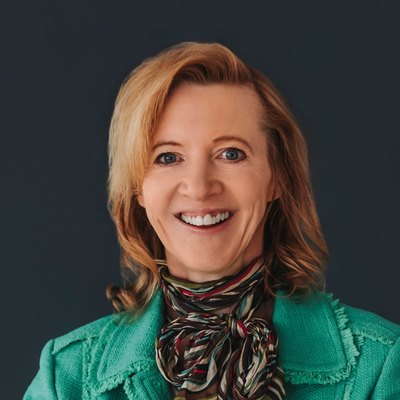
Rachel Nottingham
Governance, regulatory review and privacy
A former commercial lawyer specialising in regulatory reviews, gap analyses and effectiveness evaluations. Rachel led internal audit at a large tertiary institution, working closely with risk to provide an integrated service.
Chartered Director (IoD) · former commercial lawyer (UK qualified)
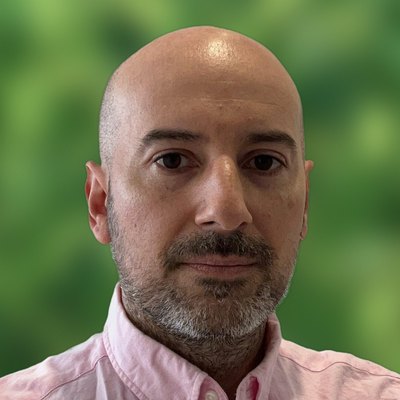
Lucas Moreno
Internal audit, technology and risk assurance
20+ years across Big Four consulting, banking and a large retail cooperative. Lucas has built internal audit, risk and compliance functions, led a national technology audit programme and delivered more than 100 audits and quality reviews.
CIA · CISA · former Associate Director, Deloitte
How we work
Senior, bounded, independent
- Senior people throughout. The people who scope the work deliver it.
- Bounded first engagements. A clear question, scope and fee, not an open-ended retainer.
- Evidence, not opinion. We tell you what we found, including when it is unwelcome.
- Independence protected. We do not sit on the committee. We disclose relevant past or current work for the organisation, assess conflicts before and throughout each engagement, and decline work where independence can't be maintained. Any management-side work for the same organisation needs a fresh conflict assessment and the client's agreement before we accept it. We don't assure our own work, including any function or controls we designed or built for the same client.
- Clear boundaries. Formal legal opinions, statutory audit, certification and other specialist work are referred to the right people.
- Written by people. Our reports and conclusions are our own; we use AI only to support analysis.
We work with tertiary and vocational education, financial services and insurance, Crown entities and not-for-profits, and local government and council organisations.
Get in touch
Most engagements start with a short conversation.
We meet in person or by video anywhere in Aotearoa New Zealand.
- John Stewart John@co-axiom.co.nz
- Rachel Nottingham rachel.nottingham@weaver.page
- Lucas Moreno lucaspablo.moreno@gmail.com
Privacy statement
We collect personal information from you, including your name and contact details, when you email us. We collect it so that we can get in touch and explore working together, and we don't share it with anyone else. You have the right to ask for a copy of any personal information we hold about you, and to ask for it to be corrected if you think it is wrong. To do either, contact Rachel Nottingham at rachel.nottingham@weaver.page.